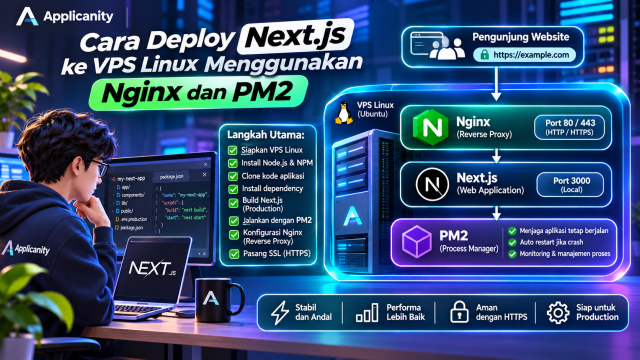
Nginx Reverse Proxy: What It Is and How It Works
When you visit a website, you usually only need to enter its address in a browser, and the page appears on your screen. However, several server components work behind the scenes to receive, process, and respond to your request.
One technology commonly used to manage this process is a Reverse Proxy. It acts as an intermediary between website visitors and the applications running on a server.
One of the most popular tools for implementing a reverse proxy is Nginx. Although Nginx is widely known as a web server, it is also frequently used as a reverse proxy because it is lightweight, fast, and capable of handling many simultaneous connections.
But what exactly is a reverse proxy? Why do so many websites and applications use it? And how does it work with Nginx?
Let's explore the concept step by step.
1. What Is a Reverse Proxy?
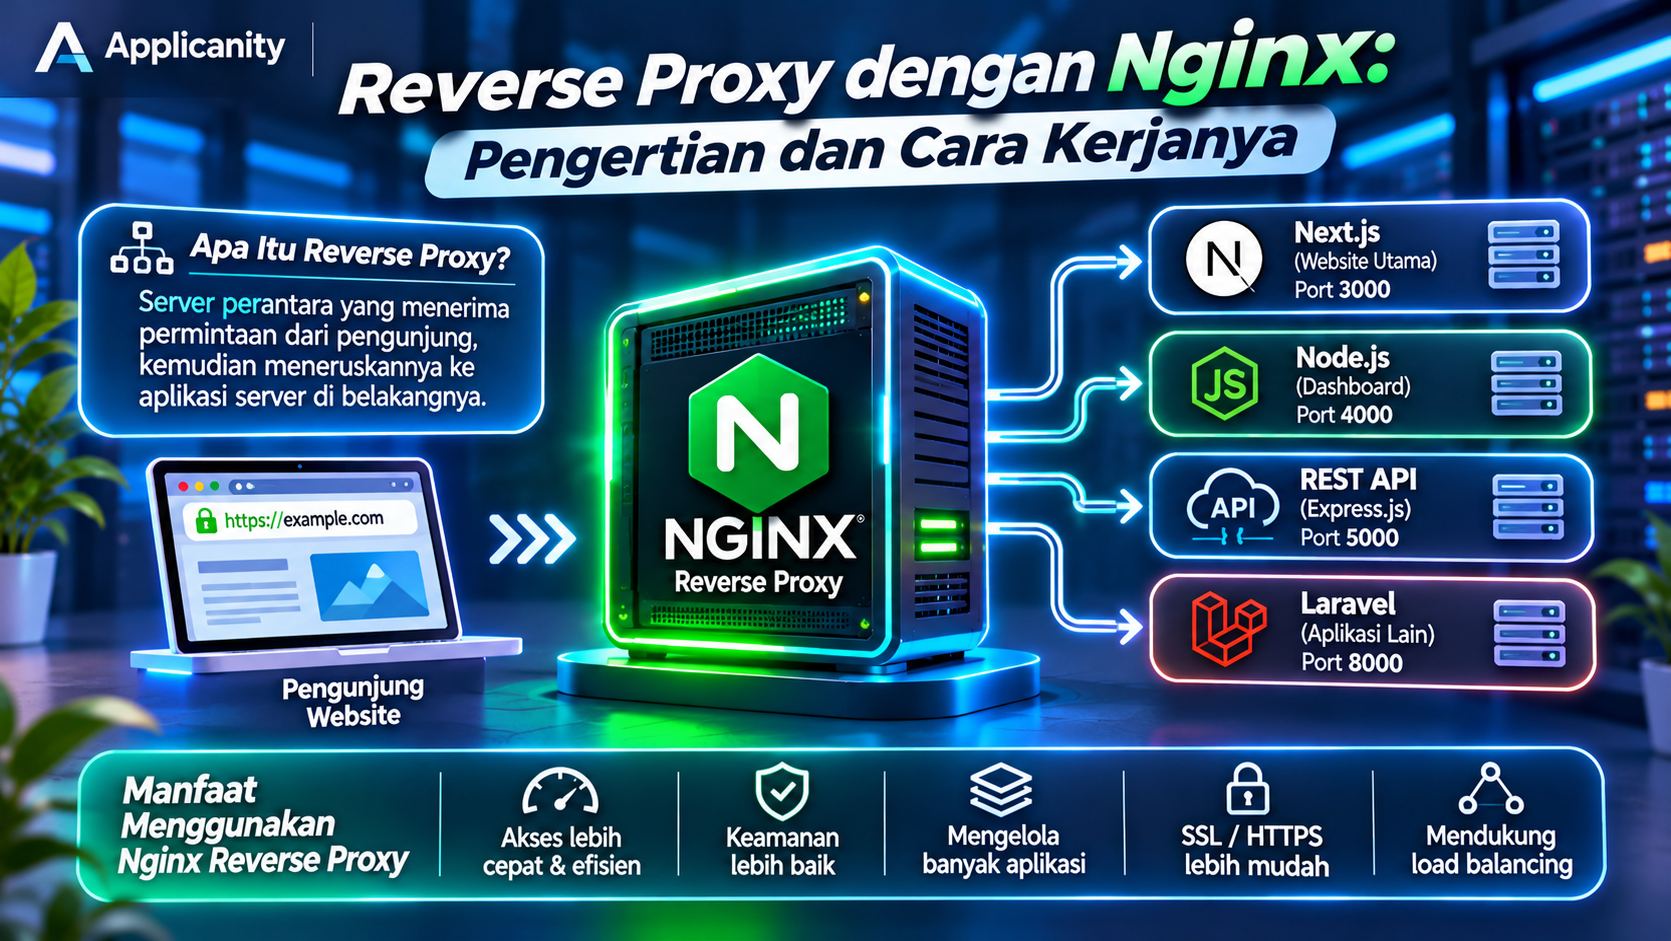
A reverse proxy is an intermediary server that receives requests from visitors and forwards those requests to the appropriate application server behind it.
To understand the concept, imagine an office with a receptionist. When someone enters the office, the receptionist welcomes them, asks what they need, and directs them to the appropriate department.
Visitors do not need to know exactly who will handle their requests. They simply communicate through the receptionist.
A reverse proxy works in a similar way. Visitors access a website through a single public address, and the reverse proxy determines which application server should receive each request.
For example, a server might run several applications:
-
The main website runs on port 3000.
-
The dashboard application runs on port 4000.
-
The API runs on port 5000.
Without a reverse proxy, visitors might need to access each application using a different address and port.
With a reverse proxy, all these applications can be accessed through domains or paths managed by a single entry point.
For example:
-
https://example.compoints to the application on port 3000. -
https://example.com/dashboardpoints to the application on port 4000. -
https://example.com/apipoints to the application on port 5000.
Visitors do not need to know which internal ports the applications use.
2. What Is the Difference Between a Reverse Proxy and a Forward Proxy?
The term reverse proxy can be confusing because another networking technology is called a forward proxy.
Both act as intermediaries in network communication, but they serve different purposes and operate on different sides of the connection.
Forward Proxy
A forward proxy works on behalf of users or devices that want to access other servers over the internet.
For example, a company might use a proxy server to manage employees' internet access. When an employee visits a website, the request passes through the proxy before reaching the destination website.
Forward proxies are commonly used to:
-
Control users' internet access.
-
Block specific websites.
-
Hide users' IP addresses from destination servers.
-
Monitor network traffic.
Reverse Proxy
A reverse proxy works on behalf of servers. When someone visits a website, the request first reaches the reverse proxy before being forwarded to the application behind it.
Reverse proxies are commonly used to:
-
Distribute requests across multiple applications.
-
Hide internal server architecture.
-
Manage HTTPS connections.
-
Improve application security.
-
Help manage server workloads.
The simplest way to remember the difference is that a forward proxy operates on the user's side, while a reverse proxy operates on the server's side.
3. How Does a Reverse Proxy Work?
To understand how it works, let's use an example of a web application running on a Linux server.
Imagine a Next.js application running on port 3000. The application can be accessed locally through http://localhost:3000.
However, we do not want visitors to access the application directly using the server's IP address and port 3000. Instead, we want them to visit https://example.com.
This is where Nginx acts as a reverse proxy.
The process works as follows:
-
A visitor opens
https://example.comin their browser. -
Nginx receives the request on the server.
-
Nginx checks the domain configuration and forwarding rules.
-
Nginx forwards the request to the Next.js application at
localhost:3000. -
The Next.js application processes the request and generates a response.
-
The response is returned to Nginx.
-
Nginx forwards the response to the visitor's browser.
Throughout this process, visitors communicate with Nginx rather than directly with the application.
Reverse Proxy Request Flow
Visitor → Nginx Reverse Proxy → Web Application → Nginx → Visitor
Nginx acts as the main entry point for incoming requests from the internet.
4. Why Use Nginx as a Reverse Proxy?
Nginx is one of the most widely used tools for managing website traffic and web applications.
In addition to serving website content, Nginx can manage communication with one or multiple applications through its reverse proxy functionality.
Here are some reasons why Nginx is commonly used.
A. Access Multiple Applications on One Server
A single VPS can host several applications at the same time. Each application can run on a different internal port.
For example:
| Application | Internal Port | Public Address |
|---|---|---|
| Next.js Website | 3000 | example.com |
| Dashboard | 4000 | dashboard.example.com |
| REST API | 5000 | api.example.com |
| Laravel Application | 8000 | laravel.example.com |
Nginx can route each domain or URL to the correct application.
This means you do not necessarily need a separate VPS for every application, as long as your server has enough resources.
B. Improve Server Security
A reverse proxy can help protect applications by limiting direct access from the internet to internal services.
For example, a Next.js application running on port 3000 does not need to expose that port publicly. Nginx can receive external connections through ports 80 and 443, then forward requests to the application through the local network.
With the correct firewall configuration, application ports can be restricted to connections originating from the server itself.
This reduces the publicly exposed attack surface and gives administrators more control over incoming traffic.
However, a reverse proxy is not a replacement for a firewall, application authentication, or security updates.
C. Manage SSL and HTTPS Connections
Nginx can handle HTTPS connections from website visitors.
For example, when someone visits https://example.com, Nginx receives the encrypted connection and can forward the request to an internal application through HTTP over the local network.
This process is commonly called SSL termination or TLS termination.
With this approach, SSL certificates can be managed at a single entry point instead of configuring certificates separately for every application.
Keep in mind that communication between Nginx and an internal application should also be protected when it travels across an untrusted network.
D. Load Balancing
Nginx can also distribute incoming requests across multiple application servers.
Imagine a website running three application instances:
-
Application server one:
localhost:3000 -
Application server two:
localhost:3001 -
Application server three:
localhost:3002
Nginx can distribute incoming requests across these instances using its load balancing functionality.
The goal is to prevent one application instance from handling all requests and to help the system handle more visitors.
E. Simplify Application Management
With a reverse proxy, visitors do not need to know technical details such as internal IP addresses, port numbers, or the technology used by an application.
You can also change the application running behind Nginx without changing the public domain used by visitors, provided the routing rules and application compatibility remain correct.
5. Example: Configuring Nginx as a Reverse Proxy
Now let's create a simple configuration that forwards a domain to a web application running on port 3000.
For this example, we will use:
-
Operating system: Ubuntu Linux.
-
Web server: Nginx.
-
Domain:
example.com. -
Application: Next.js.
-
Application port: 3000.
Make sure the application is already running and accessible through http://localhost:3000.
Step 1: Install Nginx
Run the following commands in your Ubuntu server terminal:
sudo apt update
sudo apt install nginx -y
After installation, start and enable the Nginx service:
sudo systemctl start nginx
sudo systemctl enable nginx
Check the Nginx service status:
sudo systemctl status nginx
If the service is running successfully, Nginx is ready to use.
Step 2: Create a Reverse Proxy Configuration
Create a new configuration file for your domain:
sudo nano /etc/nginx/sites-available/example.com
Add the following configuration:
server {
    listen 80;
    server_name example.com www.example.com;

    location / {
        proxy_pass http://127.0.0.1:3000;

        proxy_http_version 1.1;

        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
    }
}
Here is what the main directives do:
-
listen 80: Tells Nginx to accept HTTP connections on port 80. -
server_name: Defines the domain names handled by this configuration. -
location /: Defines the rule for requests to the root URL and its paths. -
proxy_pass: Specifies the destination application. -
proxy_set_header: Passes request information to the application.
Headers such as X-Real-IP and X-Forwarded-For help the application identify the original visitor's IP address when requests pass through a reverse proxy.
Step 3: Enable the Configuration
After creating the configuration file, enable it using a symbolic link:
sudo ln -s /etc/nginx/sites-available/example.com /etc/nginx/sites-enabled/
Next, test the Nginx configuration:
sudo nginx -t
If the configuration test succeeds, reload Nginx:
sudo systemctl reload nginx
Now, when someone visits example.com, Nginx will forward the request to the application running on port 3000.
Make sure your domain's DNS records point to your VPS public IP address.
Step 4: Enable HTTPS
To enable HTTPS, you can use Let's Encrypt with Certbot.
Install Certbot:
sudo apt install certbot python3-certbot-nginx -y
Then run:
sudo certbot --nginx -d example.com -d www.example.com
Follow the instructions until the certificate installation is complete.
After successful installation, Certbot can help add the HTTPS configuration to Nginx.
Make sure ports 80 and 443 are accessible from the internet and that your domain's DNS records point to your VPS.
6. Routing Multiple Applications with Nginx
One of the biggest advantages of a reverse proxy is its ability to manage multiple applications on a single server.
For example, imagine you have three applications:
-
The main website uses Next.js on port 3000.
-
The internal dashboard uses Node.js on port 4000.
-
The REST API uses Express.js on port 5000.
You can configure Nginx like this:
server {
    listen 80;
    server_name example.com;

    location / {
        proxy_pass http://127.0.0.1:3000;
    }
}

server {
    listen 80;
    server_name dashboard.example.com;

    location / {
        proxy_pass http://127.0.0.1:4000;
    }
}

server {
    listen 80;
    server_name api.example.com;

    location / {
        proxy_pass http://127.0.0.1:5000;
    }
}
With this configuration, all three applications can be accessed through their own domains, even though they run on the same VPS.
For production environments, these configurations should be extended with appropriate proxy headers, HTTPS settings, and security rules based on application requirements.
7. What Is the Difference Between a Reverse Proxy and a Web Server?
Nginx is often described as both a web server and a reverse proxy. This can make beginners think that these two terms mean the same thing.
In reality, a web server and a reverse proxy have different responsibilities.
A web server receives HTTP requests and delivers content to visitors. This content may include HTML, CSS, JavaScript, images, or content generated by an application.
A reverse proxy receives incoming requests and forwards them to another server or application.
For example:
-
As a web server, Nginx can directly serve HTML files and images from a website directory.
-
As a reverse proxy, Nginx can forward requests to a Next.js application running on port 3000.
Nginx can perform both functions at the same time, depending on its configuration.
8. Things to Consider When Using a Reverse Proxy
Although a reverse proxy provides many benefits, there are several things you should consider to ensure that your configuration works correctly.
A. Make Sure the Application Is Running
A reverse proxy does not automatically start your application.
If the application on port 3000 stops, Nginx will have no available destination to handle the request. Visitors may receive an error such as 502 Bad Gateway.
Make sure your application uses a process manager such as PM2 to help keep the application process running.
B. Configure Your Firewall Properly
Avoid exposing every application port to the internet without a clear reason.
If Nginx is your main entry point, visitors generally only need access to ports 80 and 443. Internal application ports can be restricted to localhost or the specific internal network that needs access.
C. Check Proxy Headers
Applications running behind a reverse proxy may need information about the original request, such as the HTTPS protocol and the visitor's IP address.
Use the appropriate proxy headers and make sure your application only trusts proxies that you control. Trusting arbitrary proxies can lead to inaccurate IP or protocol information.
D. Consider WebSocket Support
Some applications use WebSockets for real-time communication, such as live notifications, chat applications, or automatically updated dashboards.
If your application uses WebSockets, Nginx needs additional configuration to forward those connections correctly.
For example:
location / {
    proxy_pass http://127.0.0.1:3000;

    proxy_http_version 1.1;
    proxy_set_header Upgrade $http_upgrade;
    proxy_set_header Connection "upgrade";

    proxy_set_header Host $host;
    proxy_set_header X-Real-IP $remote_addr;
    proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
    proxy_set_header X-Forwarded-Proto $scheme;
}
This configuration can be used for applications that require WebSocket connections. However, the Connection header should be adjusted to match the application's connection requirements.
9. Conclusion
A reverse proxy is a useful technology for managing communication between website visitors and applications running on a server.
By using Nginx as a reverse proxy, you can host multiple applications on one VPS, manage domains, handle HTTPS connections, improve security controls, and distribute incoming requests across multiple application servers.
This approach works well for applications built with Node.js, Next.js, Laravel, Express.js, and many other web technologies.
For developers and server administrators managing multiple websites and applications, understanding reverse proxies is an important technical skill. With the right configuration, server management becomes more organized, flexible, and easier to scale.
Applicanity helps businesses build and develop digital solutions, from websites to custom applications designed around business needs.