10 Common Website Security Mistakes Developers Make and How to Avoid Them
10 Common Website Security Mistakes Developers Make and How to Avoid Them
Building a website is not just about creating an attractive design, adding useful features, or making sure every page works properly. There is another important aspect that developers should never overlook: website security.
Website security is an essential part of application development. A website without proper protection can become a target for various cyberattacks, including data theft, account hijacking, malicious code injection, and even server compromise.
Interestingly, security problems do not always happen because of highly sophisticated attacks. Many incidents actually begin with simple mistakes made during development, such as using weak passwords, exposing configuration files, or failing to validate user input.
These mistakes may seem harmless, but they can cause serious damage when exploited by malicious individuals.
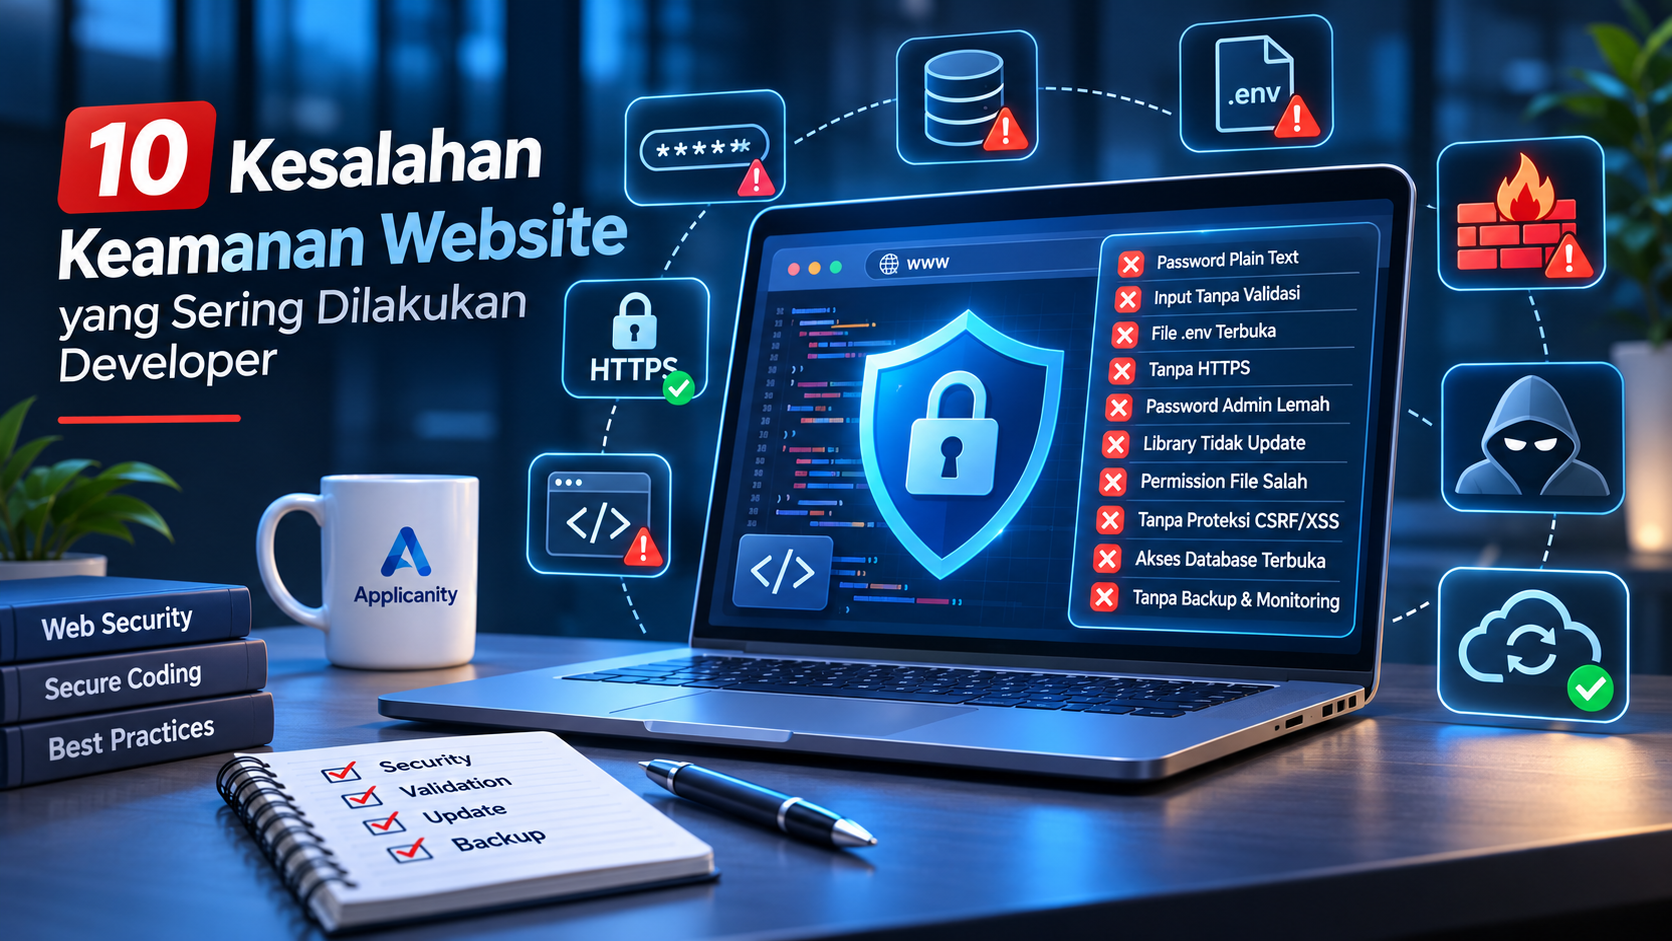
In this article, we will explore 10 common website security mistakes developers make and explain how to avoid them.
1. Storing Passwords as Plain Text
One of the most dangerous security mistakes is storing user passwords in a database without hashing them.
Some beginner developers may still store passwords directly as plain text. This is extremely risky because anyone who gains access to the database can read all stored passwords.
Imagine a website with thousands of registered users whose database gets stolen. If passwords are stored as plain text, every account could potentially be compromised.
How to avoid it:
Use password hashing algorithms specifically designed for password protection, such as Argon2id or bcrypt.
Avoid using MD5 or SHA-1 for password storage because these algorithms are too fast and are not suitable for modern password hashing requirements.
Example using PHP:
<?php

$password = "MySecurePassword123";

// Generate password hash
$hashedPassword = password_hash(
    $password,
    PASSWORD_DEFAULT
);

// Verify password
if (password_verify($password, $hashedPassword)) {
    echo "Login successful";
} else {
    echo "Incorrect password";
}
With this approach, the original password is never stored directly in the database.
2. Failing to Validate and Sanitize User Input
Websites receive different types of input from users, including usernames, email addresses, comments, contact forms, and other information.
A common developer mistake is using this input directly without checking whether it is valid or safe.
Unvalidated input can create opportunities for several attacks, including SQL Injection and Cross-Site Scripting (XSS).
For example, if a website accepts search input and directly inserts it into an SQL query, an attacker may try to inject additional SQL commands that should never be executed.
How to avoid it:
-
Validate every input according to its expected format.
-
Use prepared statements when interacting with databases.
-
Encode output before displaying it in HTML.
-
Never assume that browser input is automatically safe.
-
Perform validation on the server, even if JavaScript validation is already available in the browser.
Example using PDO prepared statements:
<?php

$email = $_POST['email'] ?? '';

$stmt = $pdo->prepare(
    "SELECT * FROM users WHERE email = :email"
);

$stmt->execute([
    'email' => $email
]);

$user = $stmt->fetch();
Prepared statements separate user-provided data from SQL commands, helping reduce the risk of SQL Injection.
3. Leaving .env Files Publicly Accessible
A .env file is commonly used to store sensitive application configuration, such as:
-
Database usernames and passwords.
-
API keys.
-
Application secrets.
-
SMTP credentials.
-
Third-party service tokens.
A common mistake occurs when developers upload .env files to production servers without making sure they are protected.
If the file can be accessed through a browser, someone may be able to read important information used by the application.
Example:
APP_ENV=production
APP_KEY=your-secret-key
DB_HOST=localhost
DB_DATABASE=my_database
DB_USERNAME=root
DB_PASSWORD=my_password
If this information is exposed, attackers may attempt to use it to gain access to databases or other services.
How to avoid it:
-
Never store
.envfiles inside publicly accessible directories. -
Make sure
.envis included in.gitignore. -
Use server configuration to protect sensitive files.
-
Never publish
.envcontents in public repositories. -
Use a secret manager when your application requires centralized secret management.
If you use a framework such as Laravel, make sure the server document root points to the public directory instead of the project root.
4. Not Using HTTPS Properly
HTTPS encrypts communication between a visitor's browser and the website server.
Without HTTPS, information transmitted over the internet may be easier to intercept, especially when users connect through insecure public networks.
The common mistake is not only failing to enable HTTPS but also enabling it without making sure the entire website uses it consistently.
For example, the homepage may use HTTPS while some resources are still loaded through HTTP. This can cause mixed content warnings.
How to avoid it:
-
Install a valid SSL/TLS certificate.
-
Make sure all website pages use HTTPS.
-
Redirect HTTP requests to HTTPS.
-
Update resource URLs, including images, CSS, and JavaScript.
-
Enable HTTP Strict Transport Security (HSTS) after HTTPS has been properly configured.
HTTPS protects data while it travels across the network, but it does not automatically protect a website against every other type of attack.
5. Using Weak Administrator Passwords
Administrator accounts are among the most important parts of a website to protect.
Unfortunately, many websites still use simple passwords such as admin123, password123, or other easily guessed combinations.
Weak passwords can become targets for brute-force attacks, where attackers automatically try multiple password combinations until they find the correct one.
Using the same password across multiple services also increases the risk. If one service experiences a data breach, other accounts using the same password may become vulnerable.
How to avoid it:
-
Use long and difficult-to-guess passwords.
-
Avoid reusing passwords across multiple services.
-
Enable Multi-Factor Authentication (MFA) for important accounts.
-
Limit repeated login attempts.
-
Use CAPTCHA or additional protection mechanisms when necessary.
-
Avoid using administrator accounts for everyday activities.
For websites with administrative dashboards, additional protection such as MFA and restricted access should be considered.
6. Ignoring Framework, Plugin, and Library Updates
Frameworks, plugins, and libraries help developers build websites faster. However, software can contain security vulnerabilities that are discovered over time.
When a vulnerability is discovered, software developers usually release updates to fix the problem.
The risk appears when developers continue using outdated versions that contain known security weaknesses.
For example, a WordPress website using outdated plugins may become a target if those plugins contain vulnerabilities that have not been fixed.
How to avoid it:
-
Update frameworks and libraries regularly.
-
Use software versions that still receive security support.
-
Remove unused plugins and packages.
-
Check security advisories for your dependencies.
-
Test updates before applying them to production servers.
-
Use dependency scanning tools to identify vulnerable libraries.
Do not delay security updates unnecessarily, especially when a critical vulnerability has already been identified and an official patch is available.
7. Ignoring File and Directory Permissions
Every file and directory on a server has permission settings that determine who can read, write, or execute it.
A common mistake is assigning overly permissive permissions just to make an application work without errors.
For example, using permission 777 on application directories.
This permission allows all user categories to read, write, and execute files. If used carelessly, it may allow unauthorized users to modify application files.
How to avoid it:
-
Set permissions according to application requirements.
-
Avoid using permission
777unless there is a clearly justified need. -
Make sure sensitive configuration files are accessible only to authorized users.
-
Configure file ownership correctly for your web server.
-
Separate public directories from internal storage directories.
Examples of commonly used starting permissions:
# Regular file
chmod 644 index.php

# Directory
chmod 755 public/

# Sensitive file
chmod 600 .env
Permission requirements may vary depending on the application and server configuration. Make sure the web server can still access the files it needs.
8. Failing to Protect Against CSRF and XSS Attacks
CSRF and XSS are two common types of attacks that affect web applications.
Cross-Site Request Forgery (CSRF) occurs when an attacker attempts to make a user's browser send an unwanted request while the user is authenticated.
Cross-Site Scripting (XSS) happens when an attacker manages to inject malicious JavaScript into a website page, causing it to execute in visitors' browsers.
Both attacks can create serious problems, especially on websites with login systems, administrative dashboards, or transaction features.
How to avoid it:
To prevent CSRF:
-
Use CSRF tokens in forms and requests that modify data.
-
Verify tokens on the server.
-
Configure cookies with appropriate SameSite attributes.
-
Do not use GET requests for operations that modify data.
To prevent XSS:
-
Encode data before displaying it in HTML.
-
Never insert untrusted user input directly into JavaScript or HTML.
-
Use Content Security Policy (CSP) as an additional layer of protection.
-
Avoid using
innerHTMLwith untrusted data unless it has been properly sanitized.
Many modern frameworks already provide CSRF protection and automatic output escaping. However, developers still need to understand how these protections work and avoid disabling them without a valid reason.
9. Exposing Databases and Admin Panels to the Internet
Databases and administrator dashboards are important parts of a website. They should not be freely accessible to everyone.
Incorrect server configurations may expose database ports such as MySQL or PostgreSQL to connections from the public internet.
The same problem can happen when administrative tools such as phpMyAdmin or internal dashboards are accessible without proper access restrictions.
If an attacker discovers these services and gains unauthorized access, the consequences can be extremely serious.
How to avoid it:
-
Restrict database access to servers or networks that actually need it.
-
Never expose database ports to the entire internet without a valid requirement.
-
Use firewalls to restrict incoming connections.
-
Protect administrative panels with strong authentication.
-
Use VPNs or IP allowlists for administrative access when possible.
-
Disable services that are not being used.
-
Monitor access logs for suspicious activity.
For example, a MySQL database used only by an application on the same server should generally be configured to accept local connections only, if remote access is not required.
10. Failing to Perform Backups and Security Monitoring
The final common mistake is assuming that website security is complete once the application has been launched.
In reality, website security is an ongoing process.
Websites can experience various problems, including database corruption, configuration errors, ransomware attacks, or accidental file deletion.
Without backups, recovery can become extremely difficult and time-consuming.
Additionally, without monitoring, suspicious activities may remain unnoticed until damage has already occurred.
How to avoid it:
-
Schedule regular backups of website files and databases.
-
Store backup copies separately from the main server.
-
Encrypt backups containing sensitive information.
-
Test backup restoration regularly.
-
Monitor application and server logs.
-
Use monitoring systems to detect suspicious activities.
-
Prepare an incident response procedure.
Remember, a backup that has never been tested may not work when you actually need it.
Conclusion
Website security is not only the responsibility of security teams or server administrators. Developers also play an important role in making sure that applications do not contain vulnerabilities that can be exploited by malicious individuals.
The ten mistakes discussed above show that many security problems can actually be prevented during the early stages of development.
From properly hashing passwords and validating user input to protecting configuration files, using HTTPS, updating libraries, and restricting server access, every step contributes to a more secure website.
Developers should not focus only on making features work. They should also make sure those features are built with security in mind.
By adopting secure development practices from the beginning, you can reduce the risk of attacks and maintain user trust in your website.
Need a secure, stable, and professional website?
Applicanity provides website and application development services with a focus on code quality, performance, and system security. We help businesses build digital solutions that not only work properly but also have a technical foundation that supports long-term growth.
Visit Applicanity to learn more about our website development and digital solution services.